Many frameworks, many years, many departments — one platform, the whole picture
Shared controls, shared evidence, continuity year over year; executives see accountability and risk; data never leaves your data center.
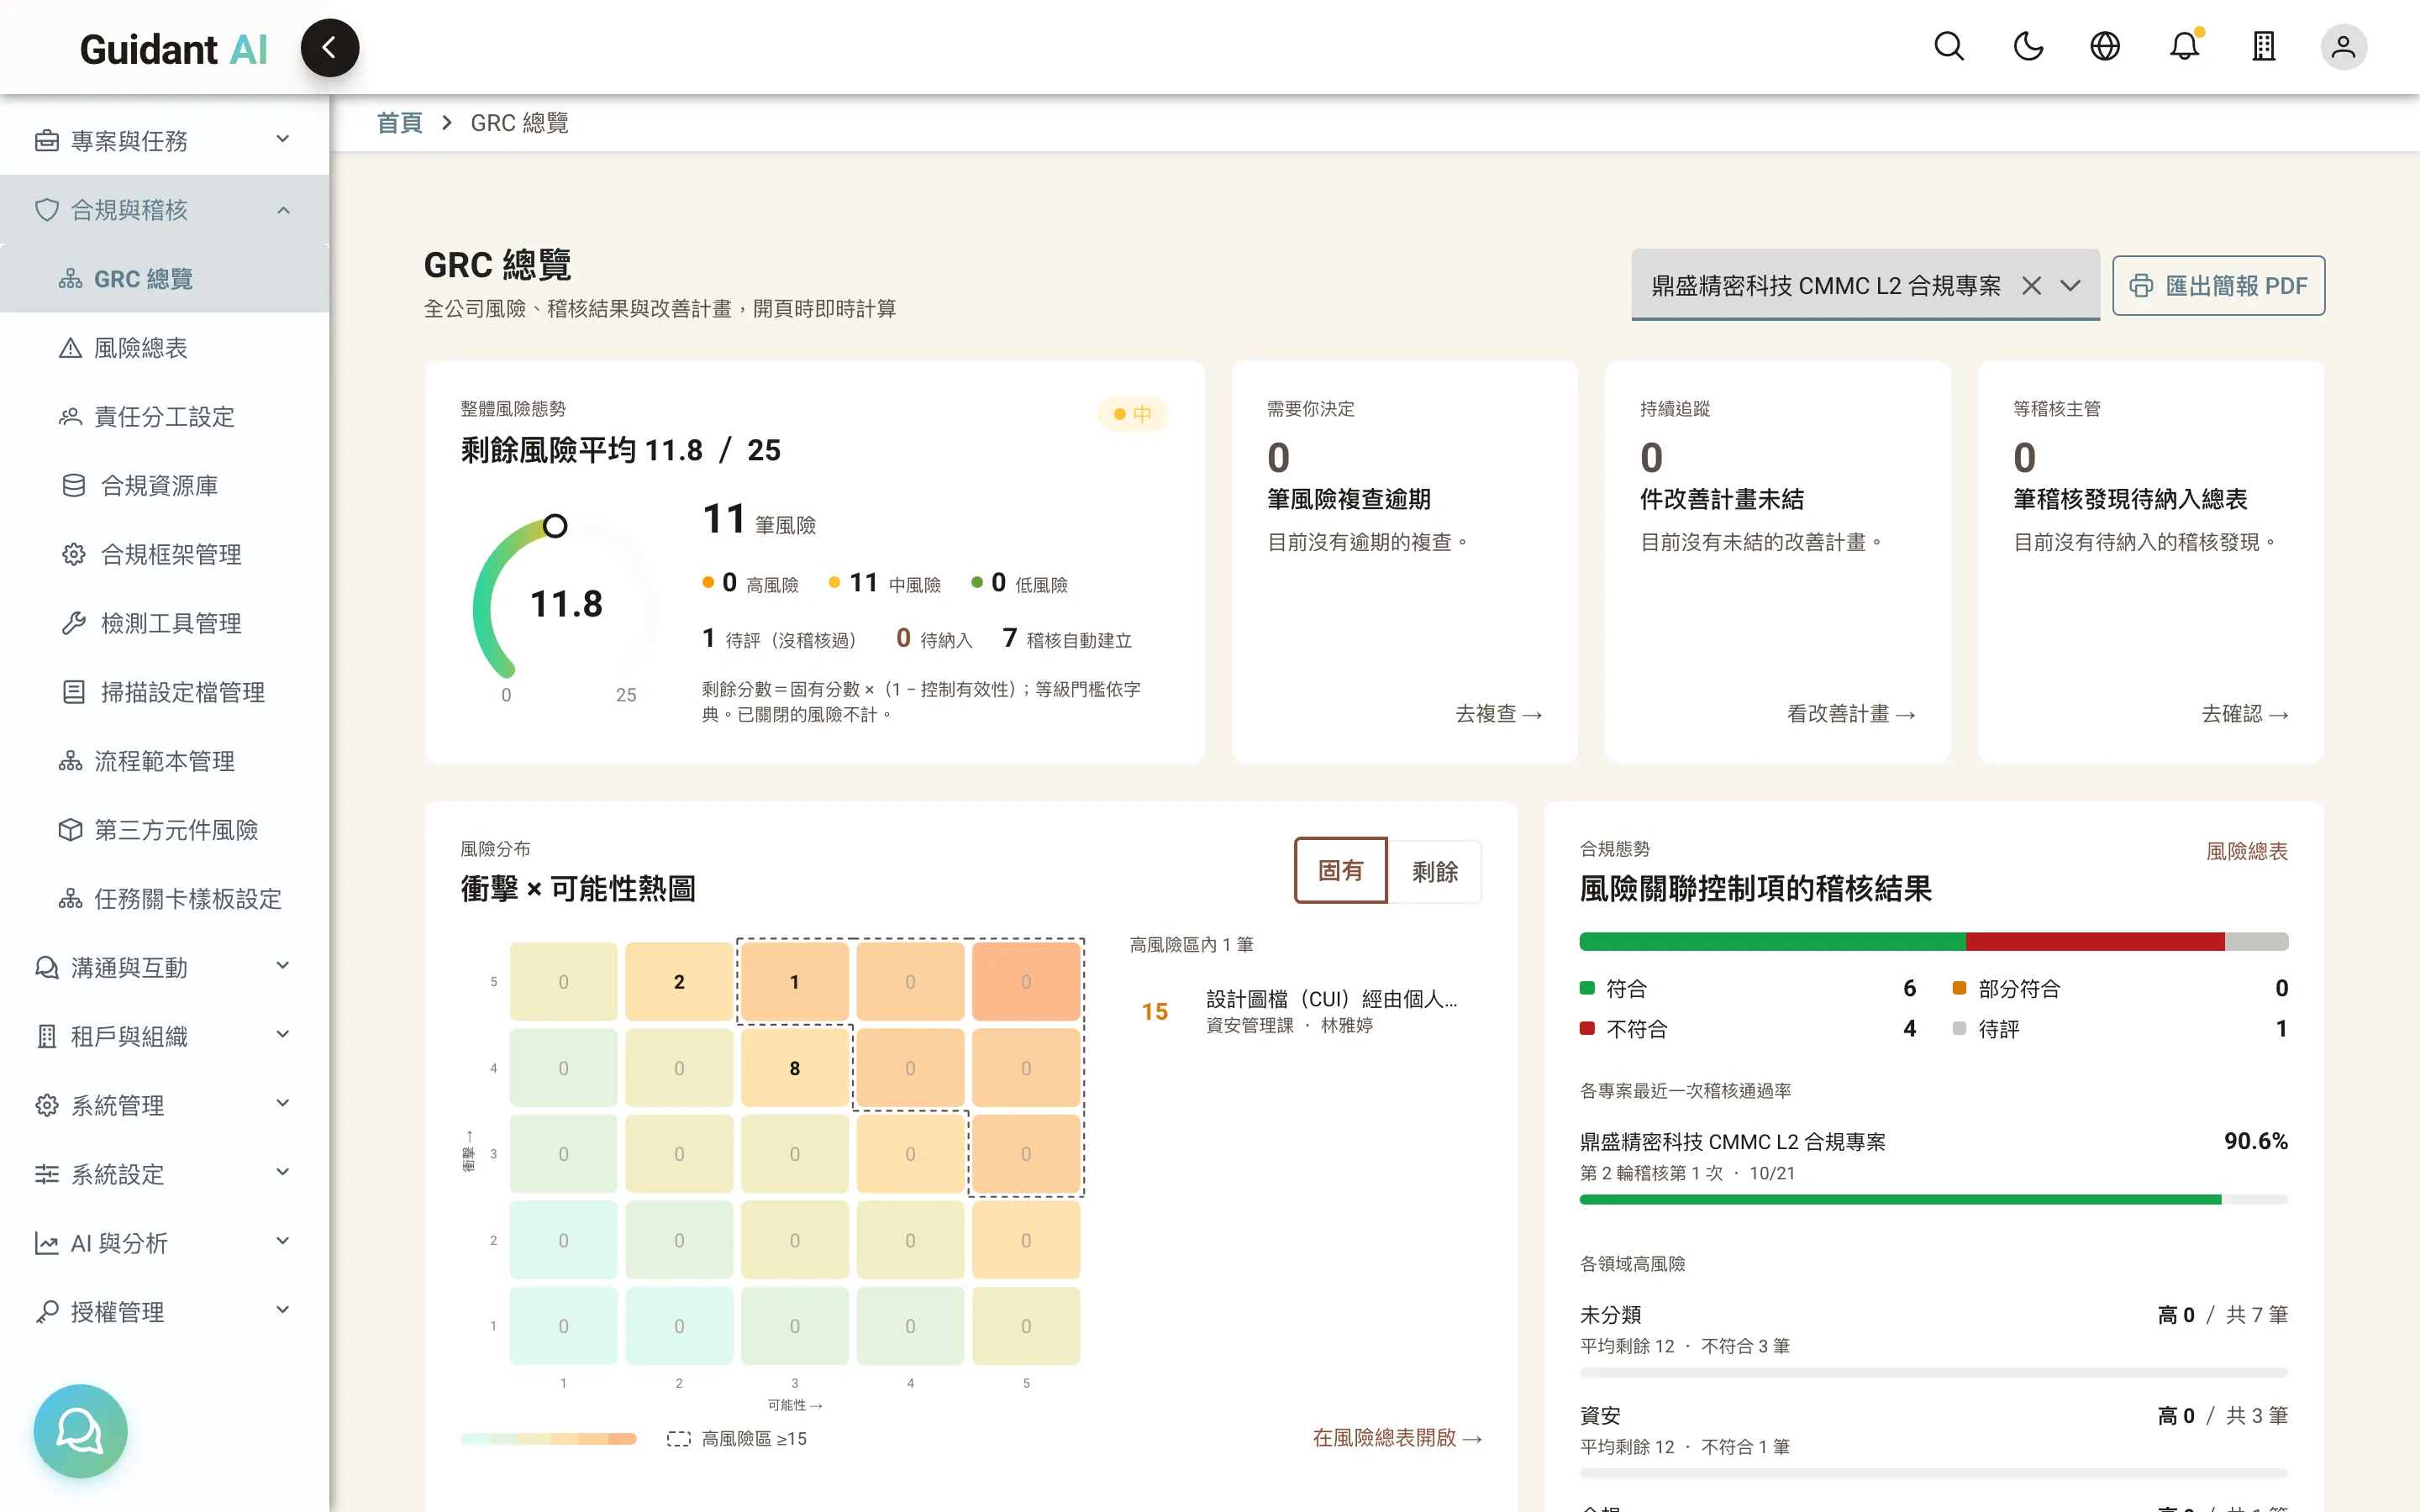
Your day
- Morning
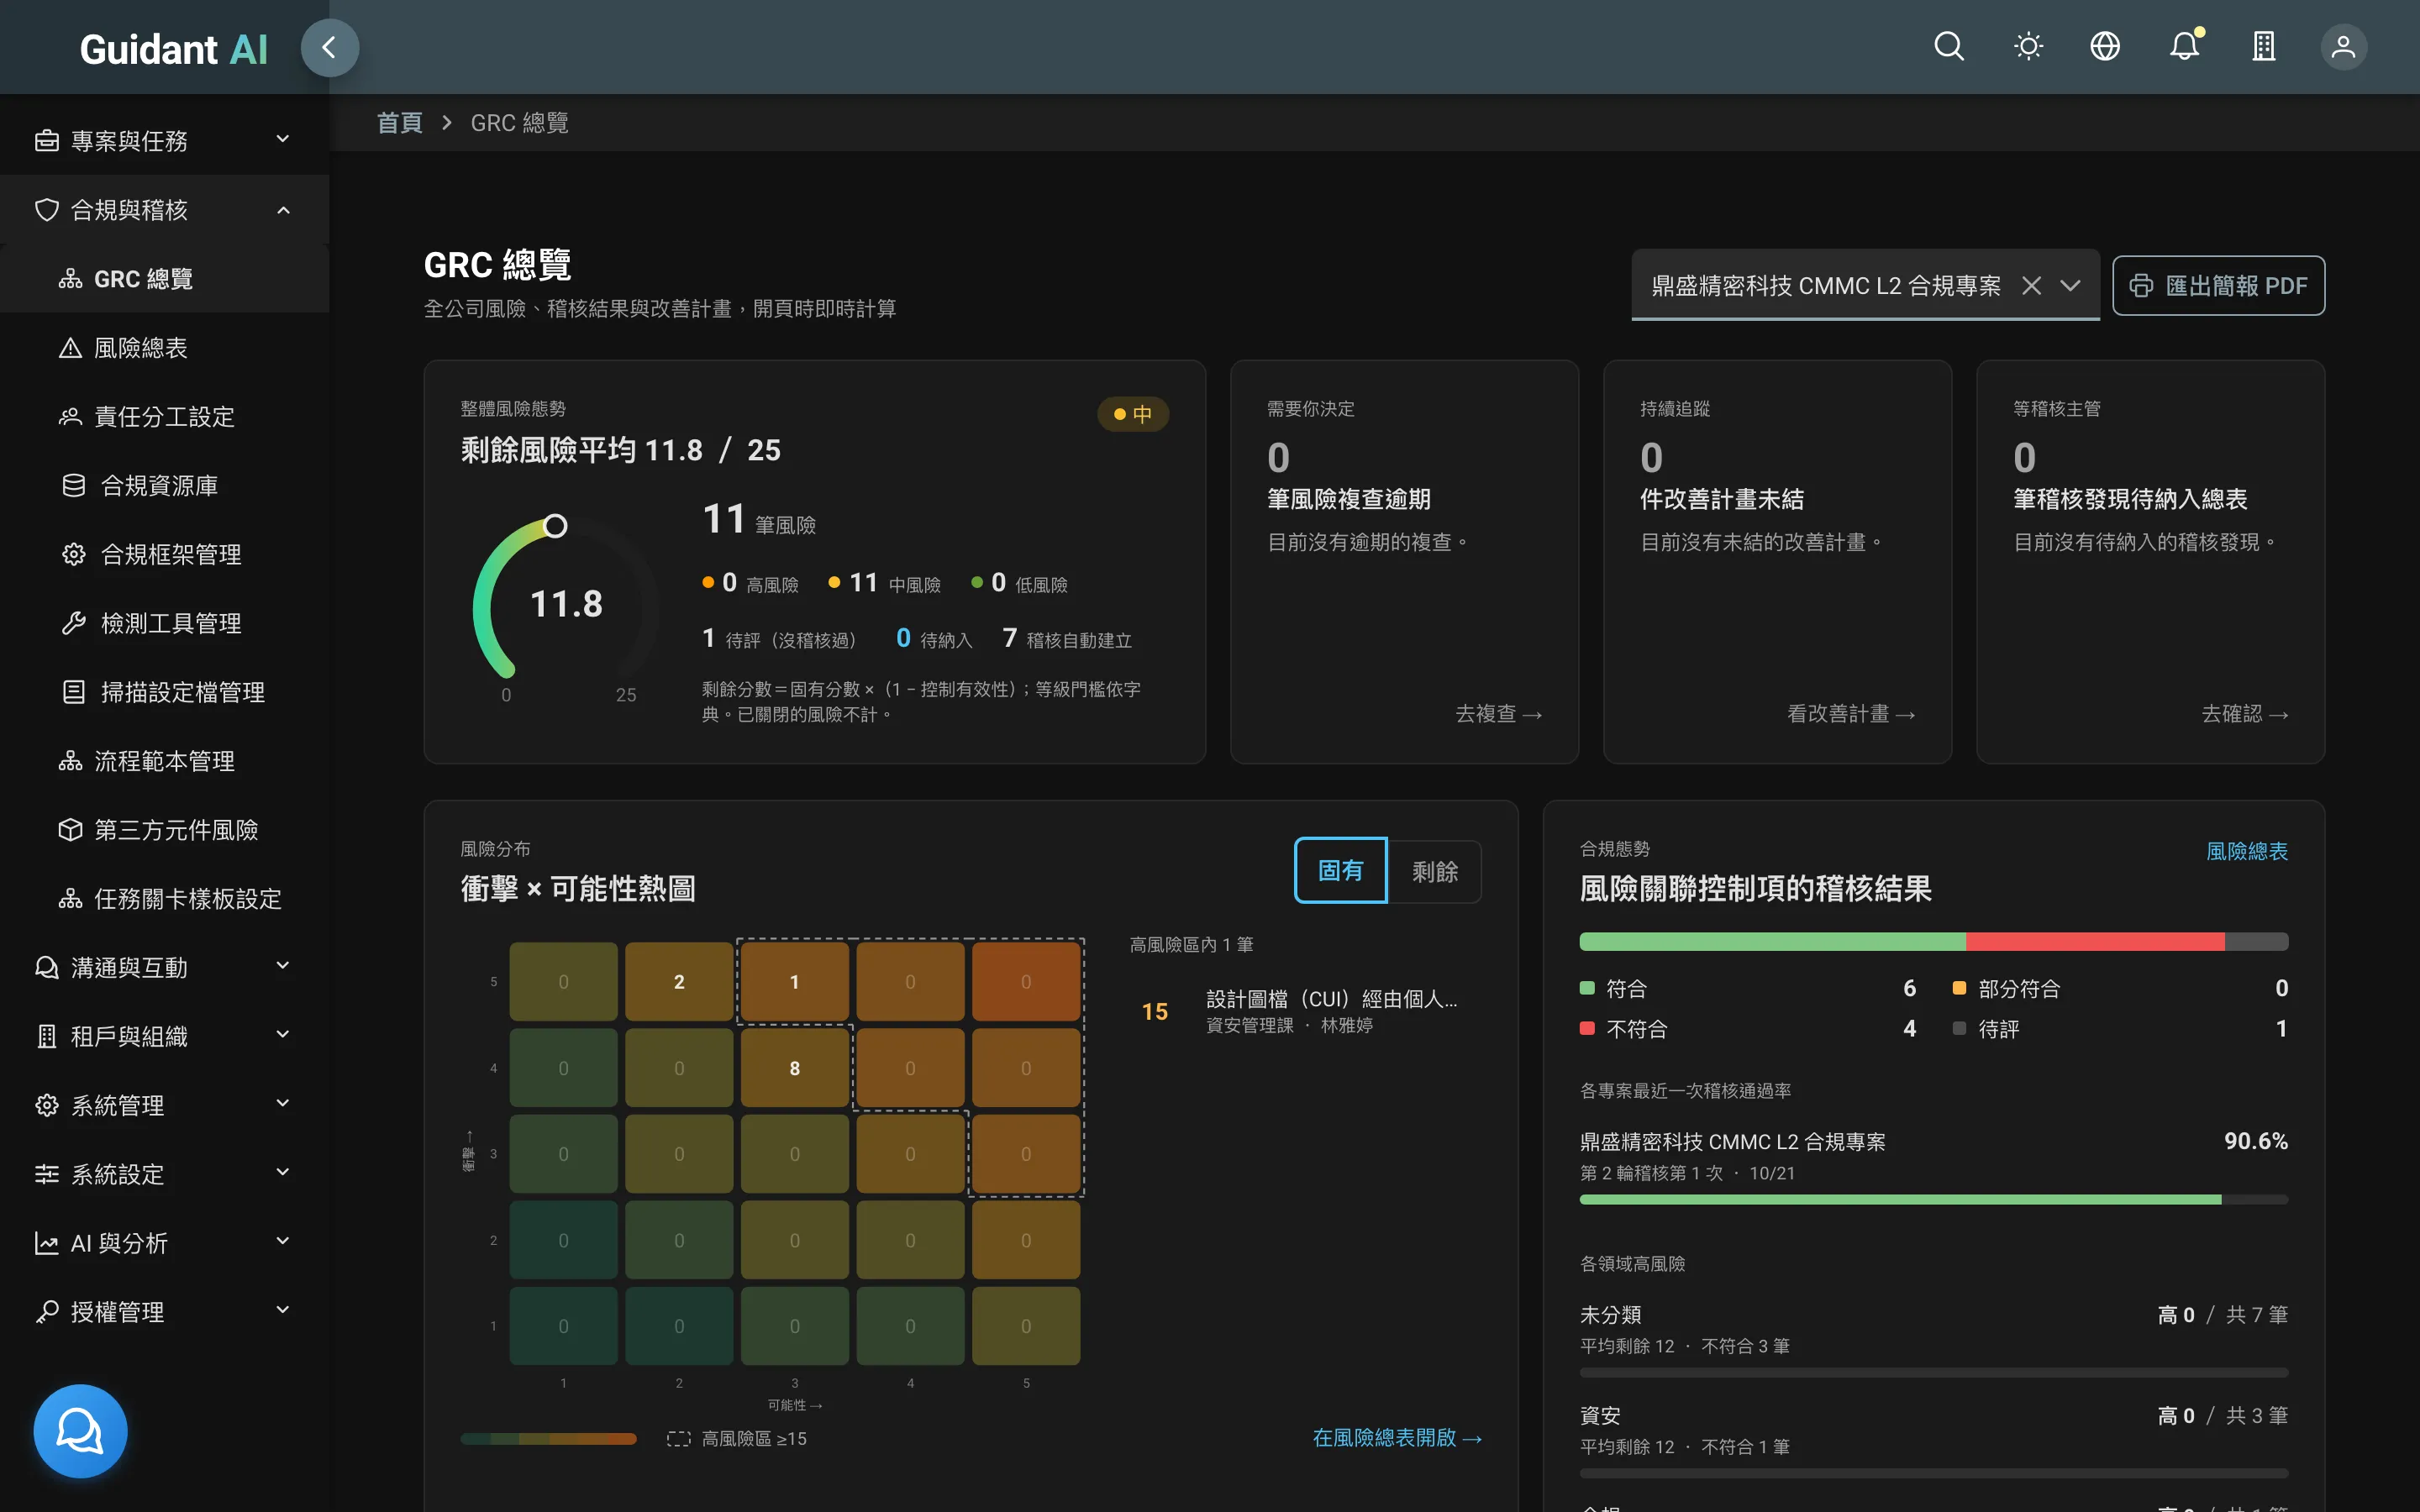
- The GRC overview shows IT has three open high risks; click through to the remediation plans.
- Late morning
- The ISO 27001 surveillance audit is next month; last year's evidence is all there, only this year's changes to add.
- Afternoon
- Legal asks about CRA readiness; open the CRA project dashboard and send a screenshot.
- End of day
- Quarterly checks open automatically for each department; the system reminds them before the due date.
Three scenarios
Shared controls across frameworks
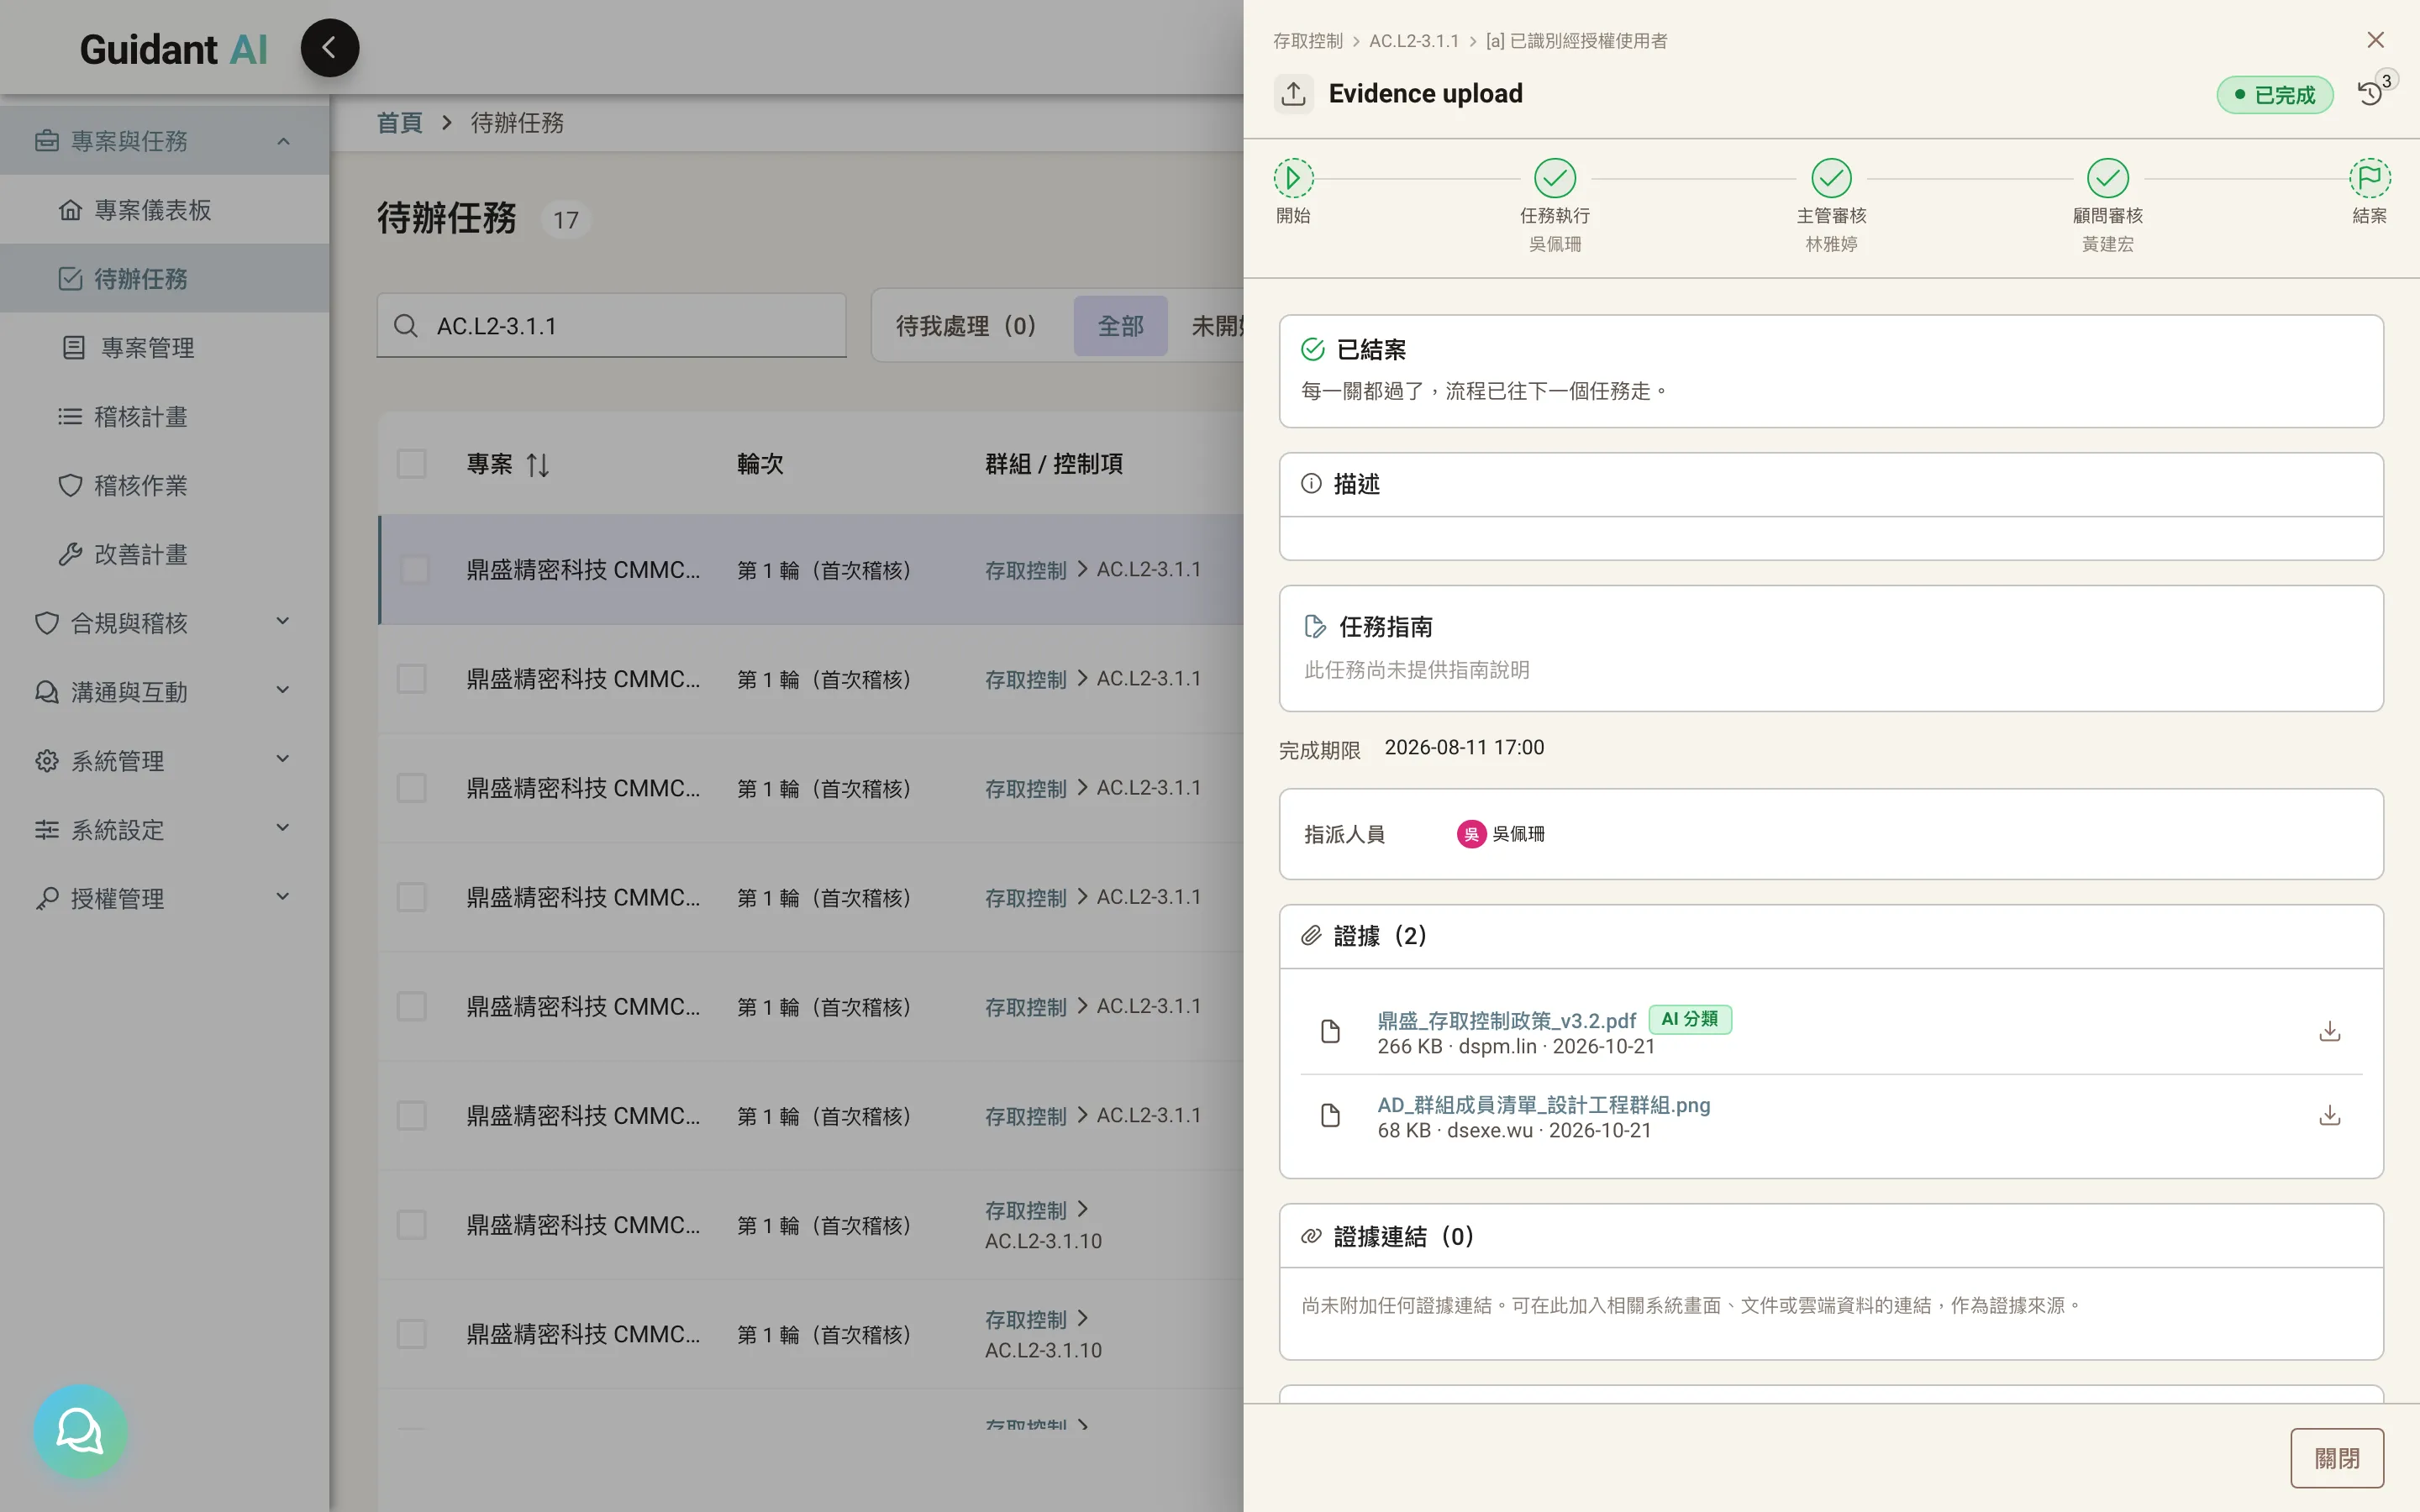
Run ISO 27001, CMMC and CRA as separate projects; where controls overlap, evidence is shared. One vulnerability scan report serves all three.
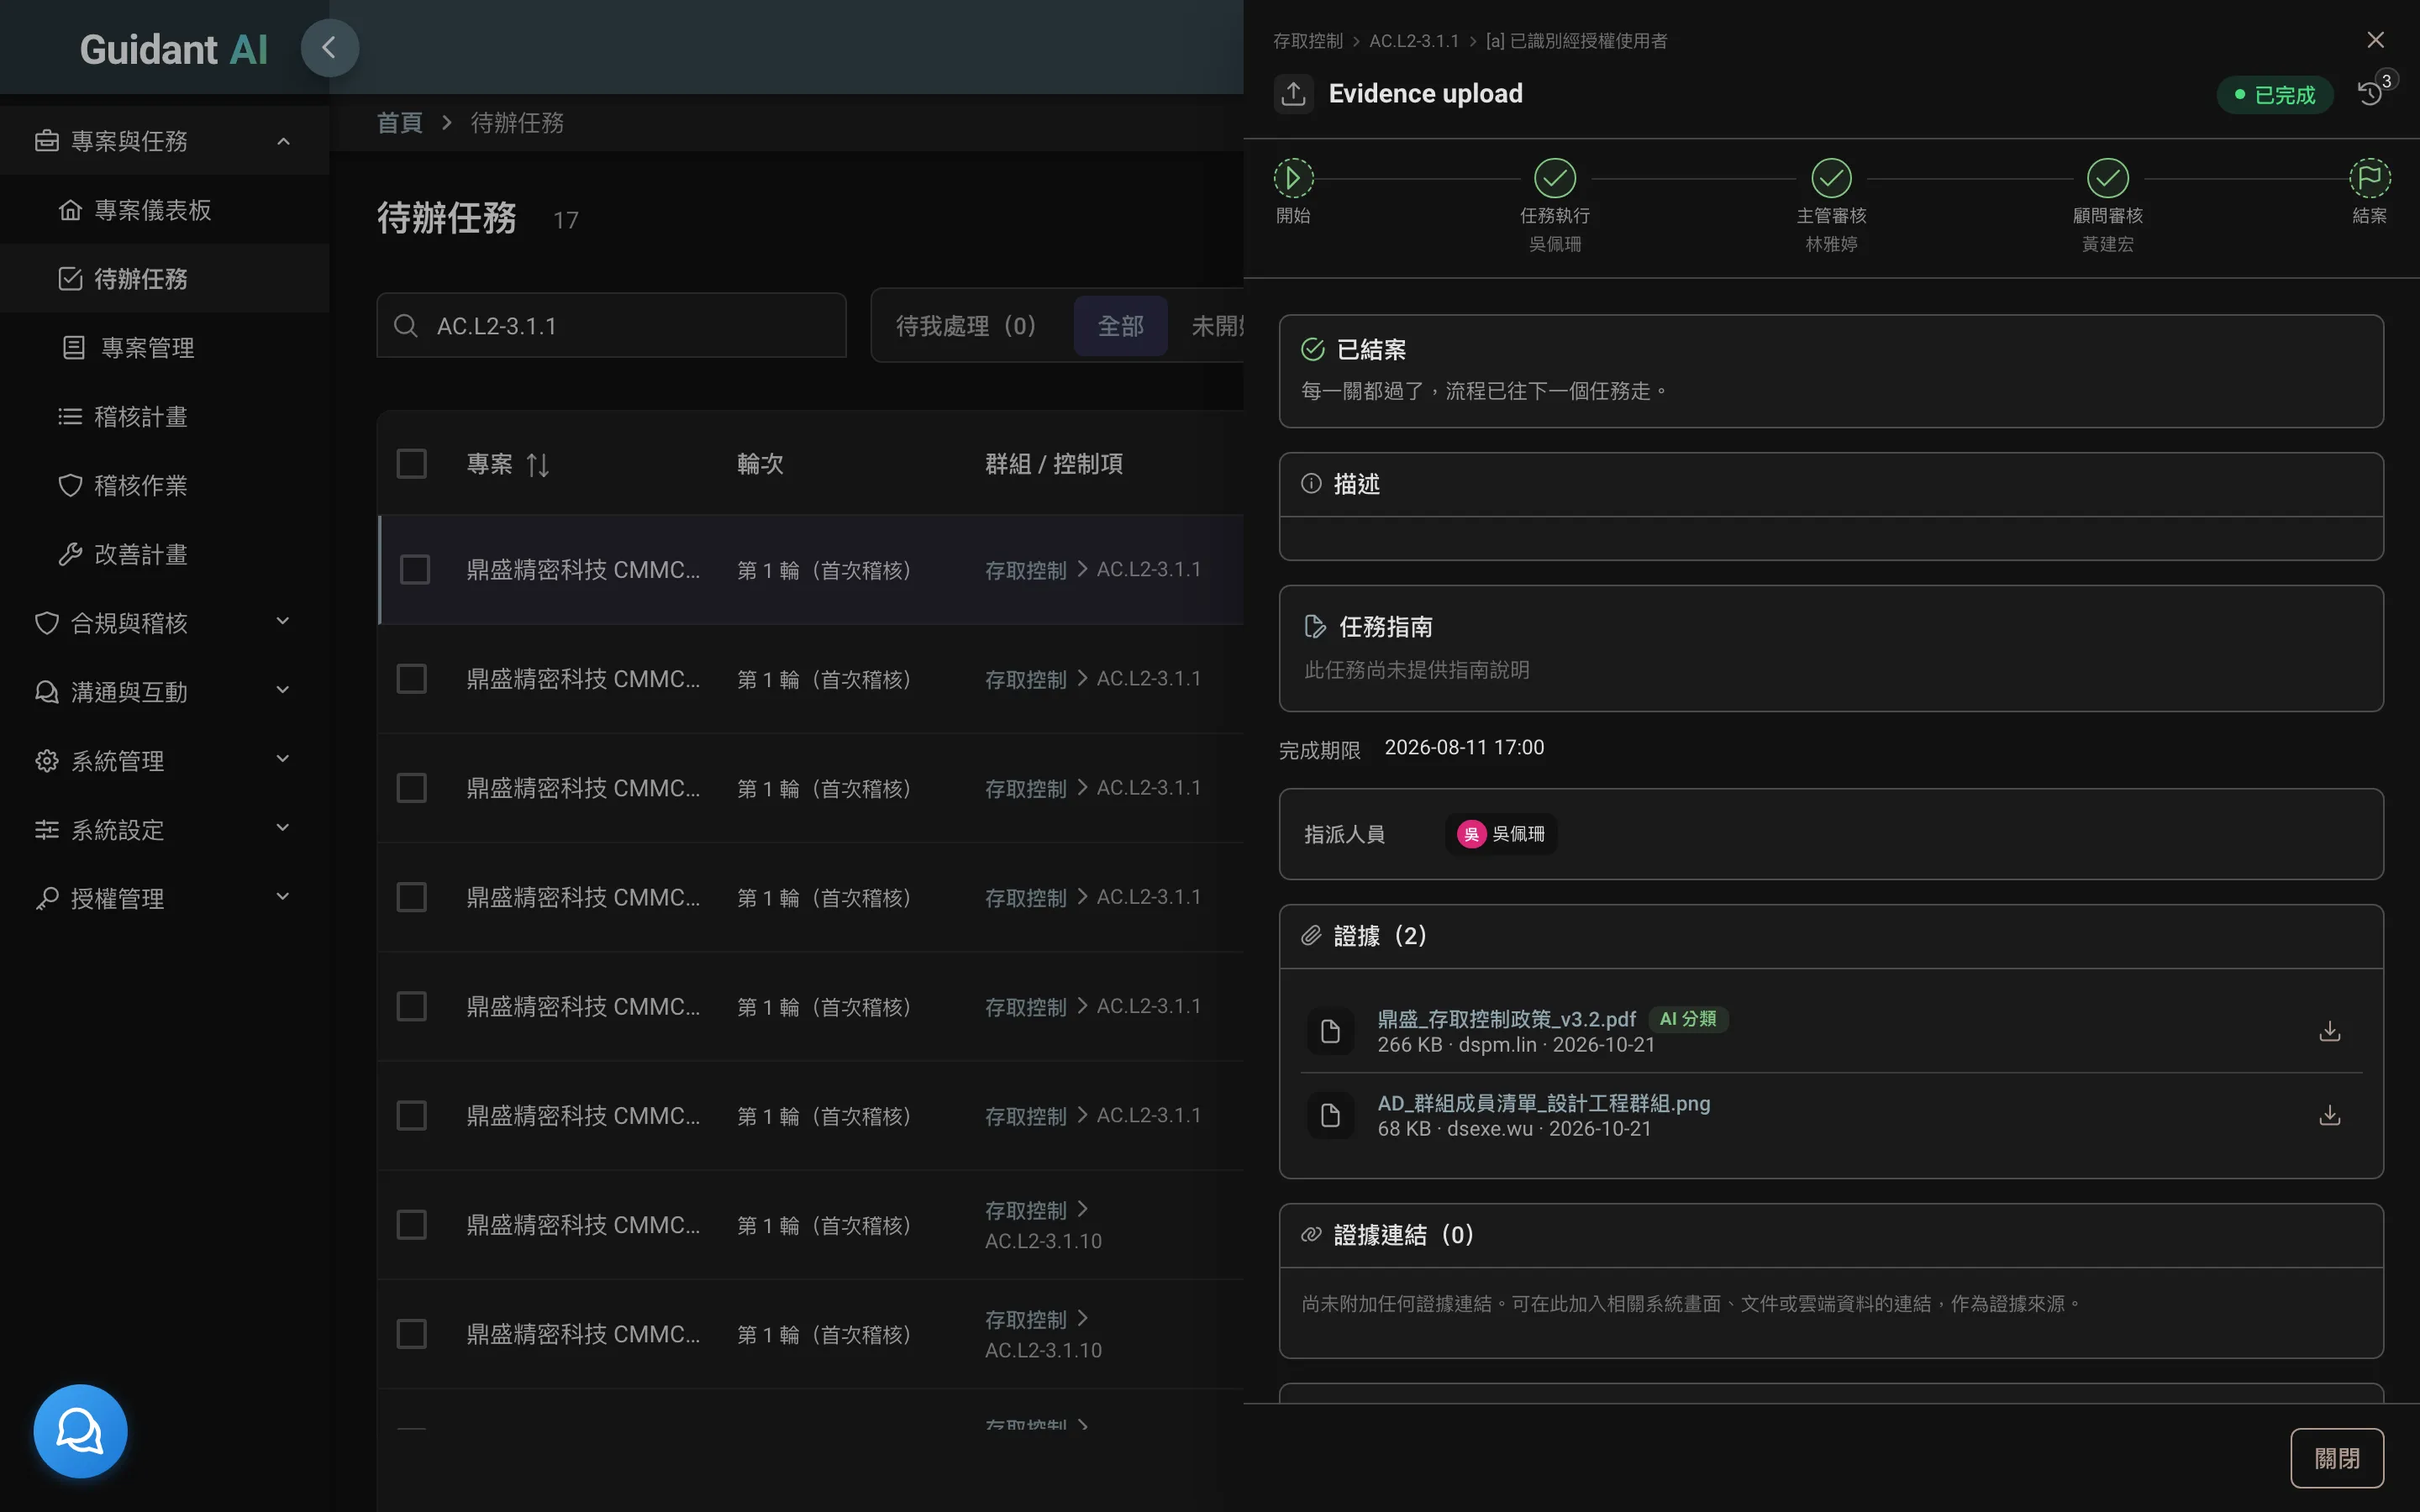
Screenshot: Evidence shared across projects
Cross-department ownership
Map the department tree to controls; every control has an owner. Review gates run doer → manager → auditor; the responsibility matrix (RACI) goes into the closing report.
Data stays on premises
Installed as a whole on your Linux host, connected to your LDAP, SIEM and notification systems. Only the frontend is exposed; evidence is unpacked in a sandbox; AI calls go through a masking gateway.
Screenshot: Deployment architecture
Frequently asked questions
One. Use five tenants or five department trees, depending on how much isolation you need.
Related guides
Go to the compliance guides →