Entering the US defense supply chain starts with managing 110 controls
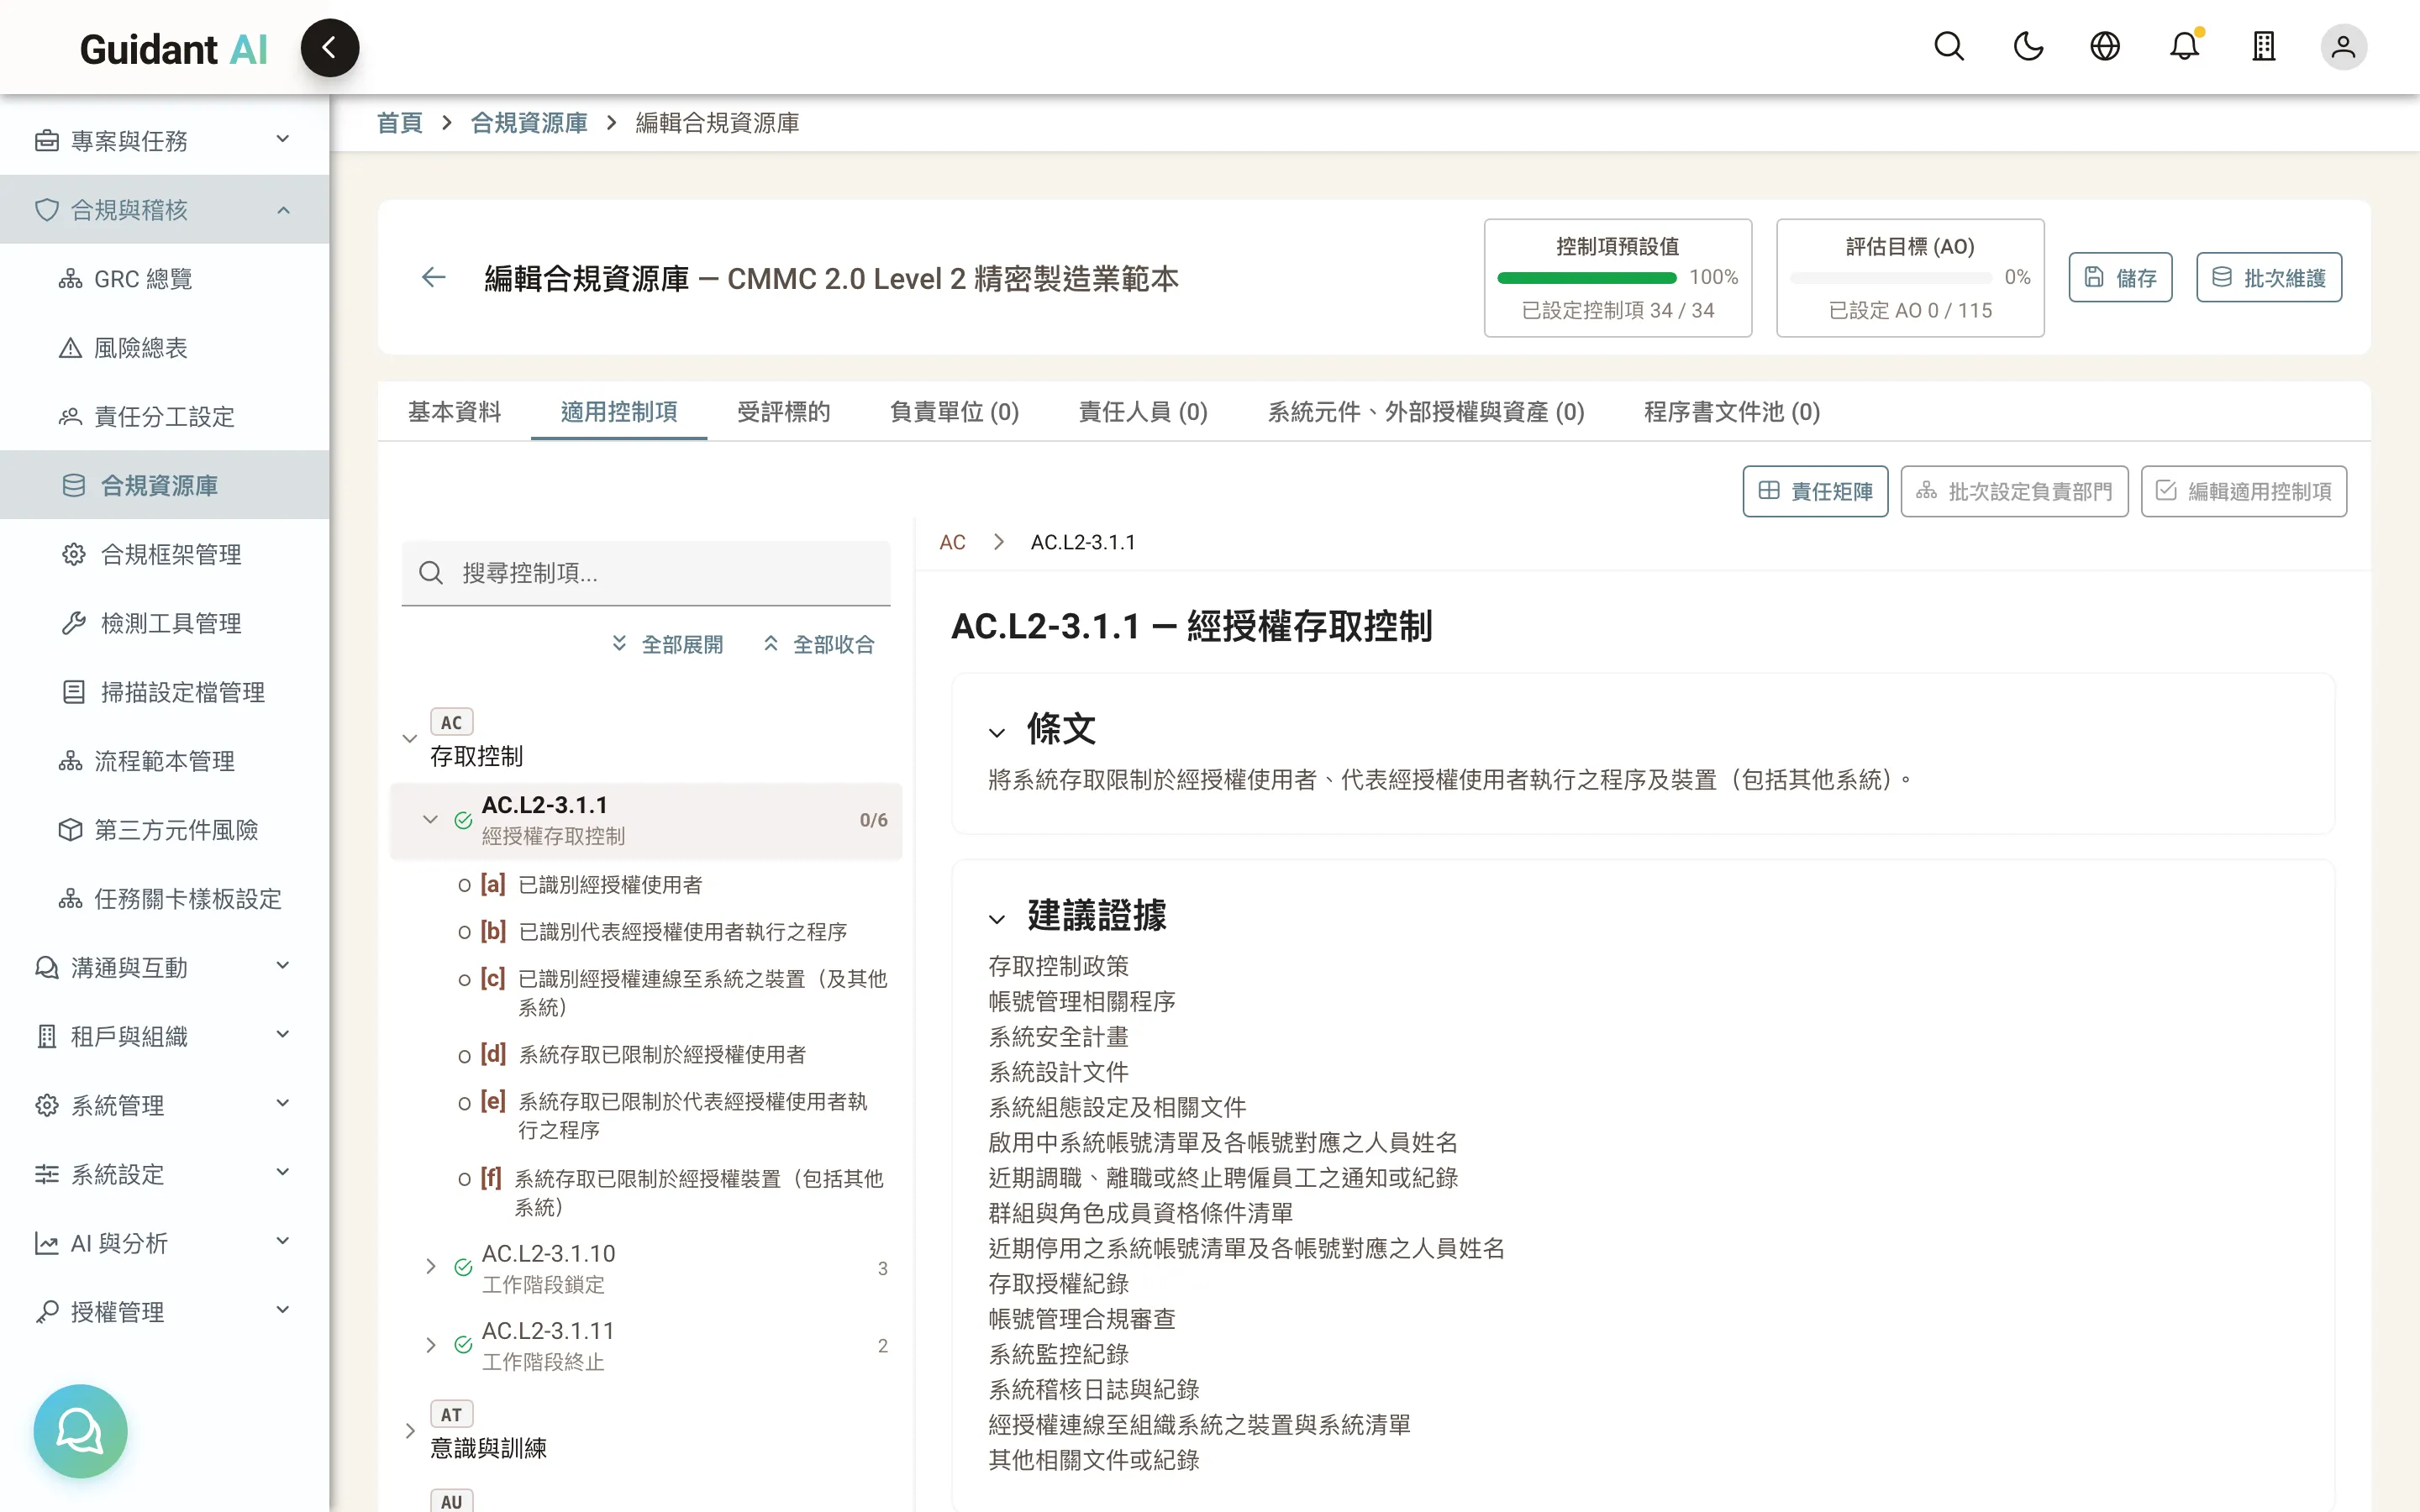
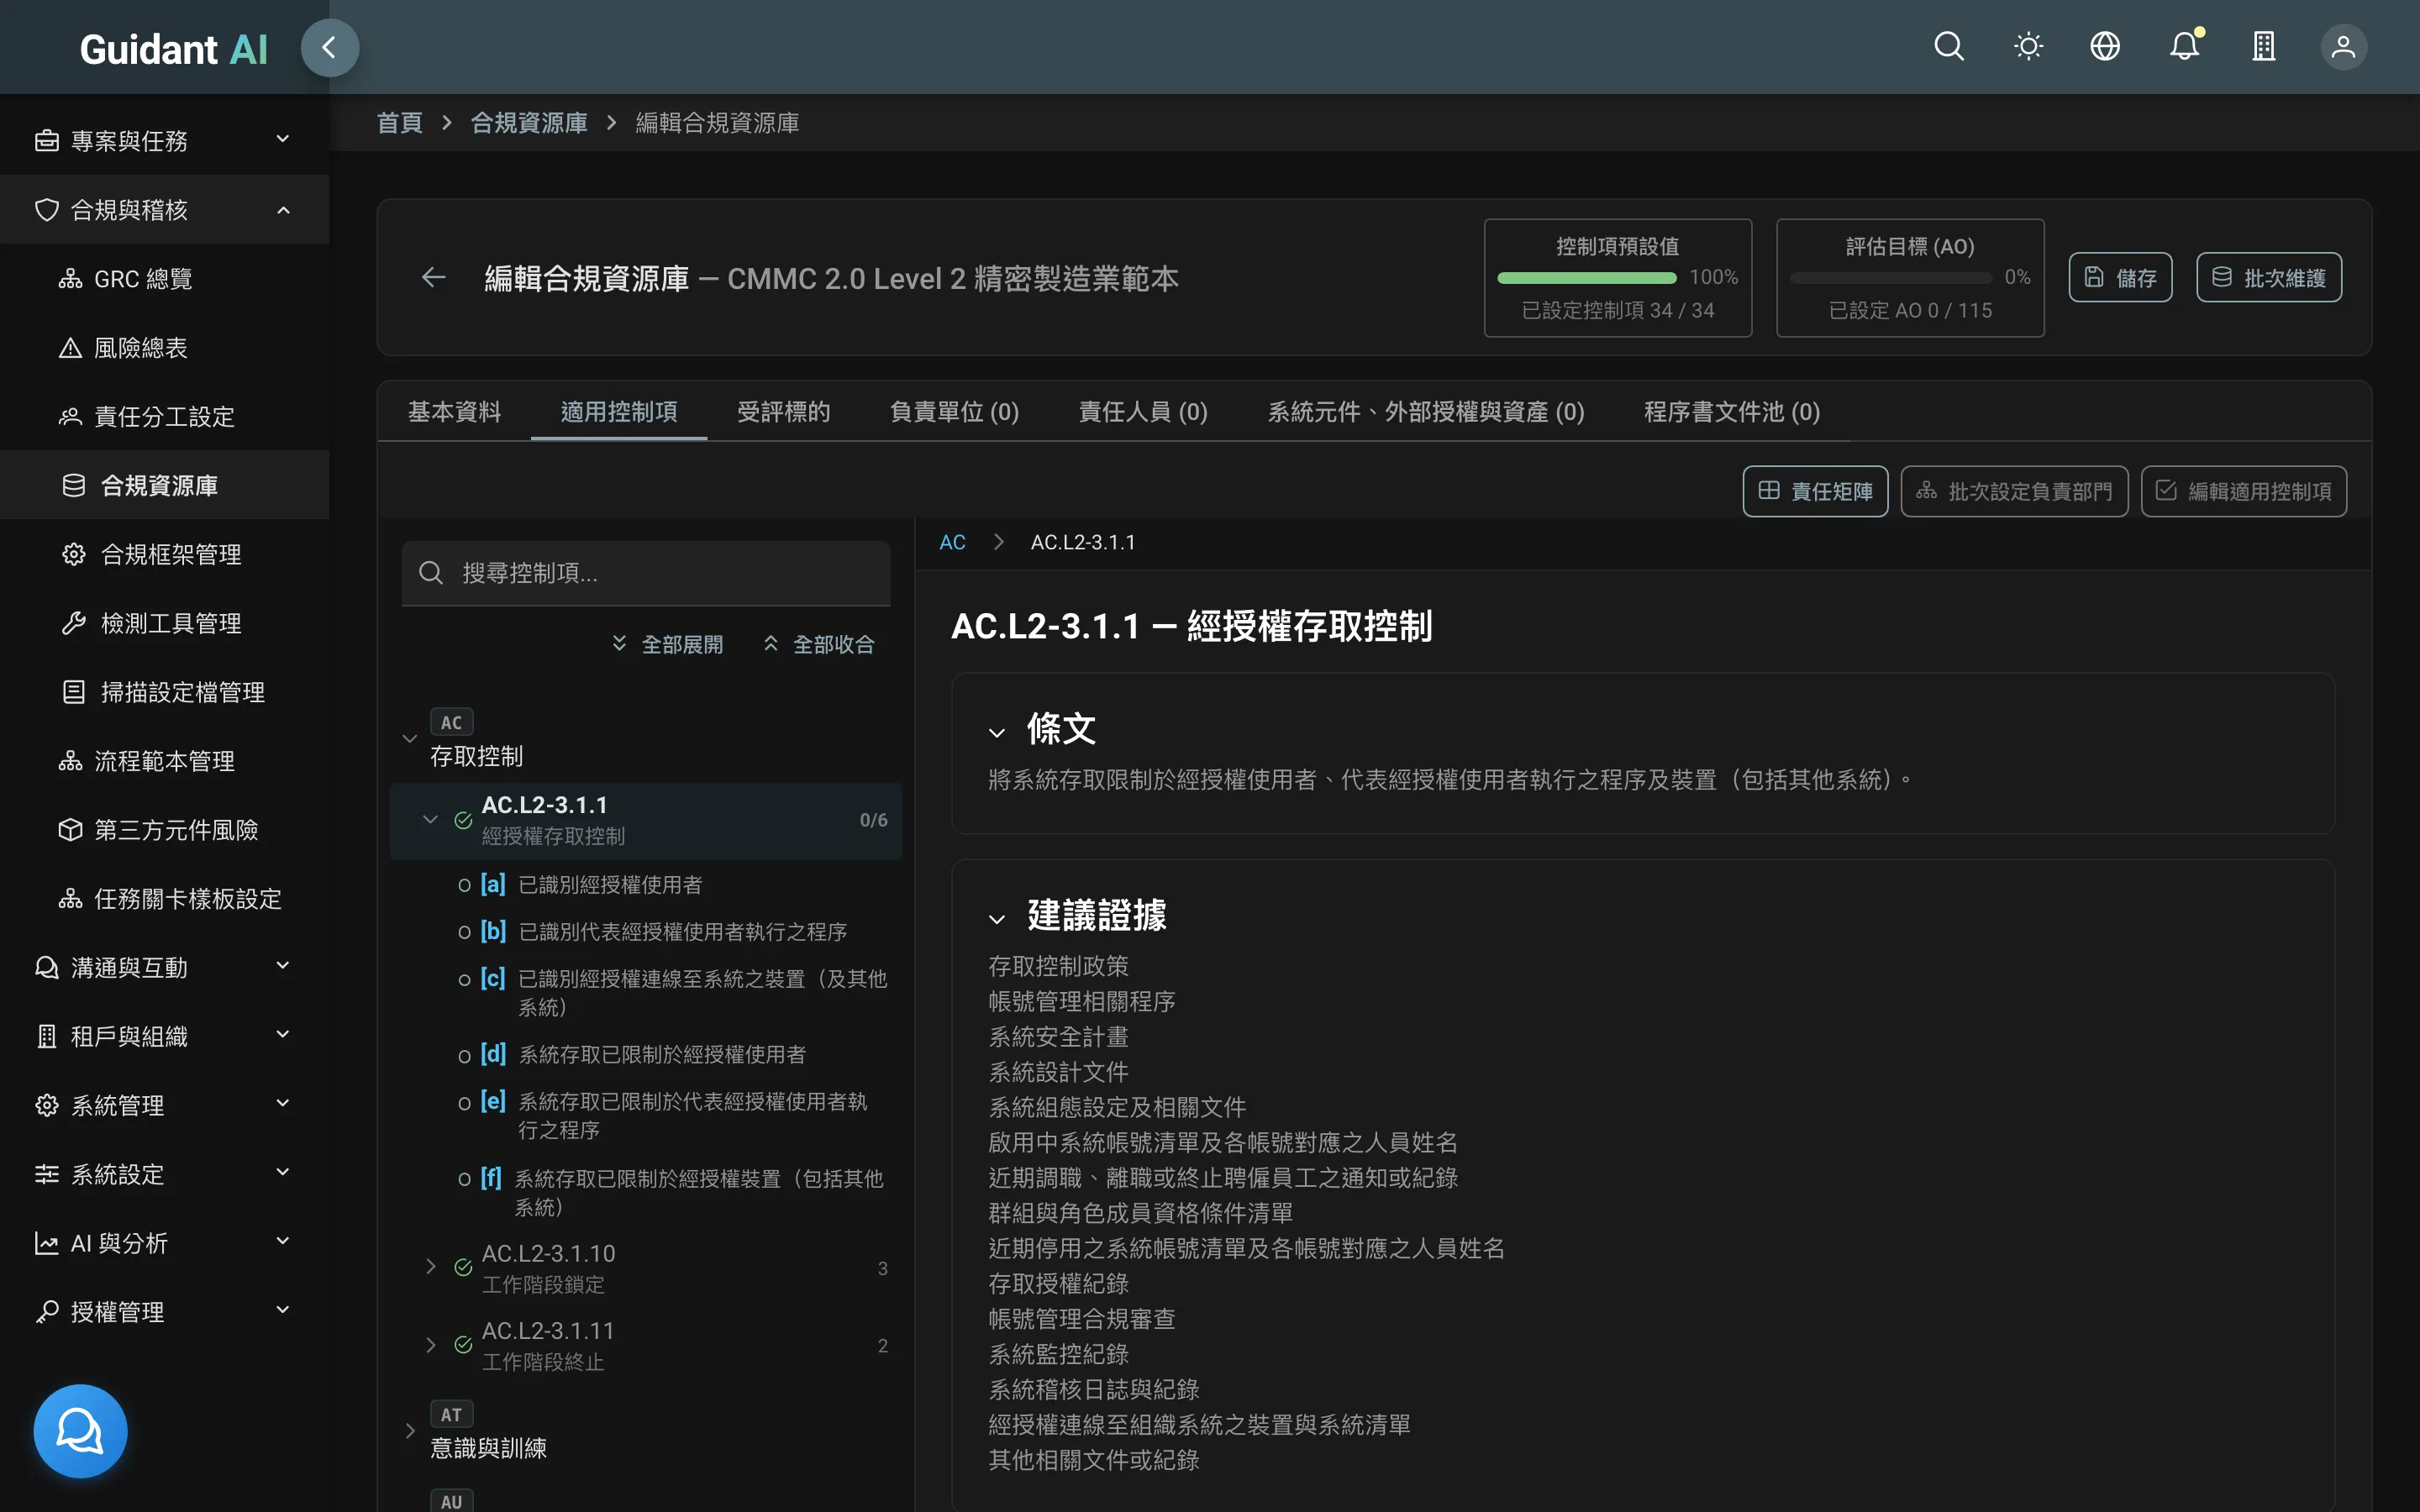
Guidant AI ships with CMMC 2.0 built in — SSP, evidence, self-assessment and C3PAO readiness on one line.
What the framework asks of you
01
Write a System Security Plan (SSP)
For all 110 Level 2 controls, state how you do it today. It's the first document an assessor reads.
02
Produce evidence
Every assessment objective (AO) needs proof — policies, configuration screenshots, logs.
03
Plan remediation (POA&M)
List what isn't done yet, schedule it and close it within the allowed window.
Read more: What is CMMC
How Guidant AI maps to it
| Framework requirement | Guidant AI |
|---|---|
| 110 controls, 320 assessment objectives | Built-in CMMC 2.0 Level 2 framework; controls tree with every AO and suggested evidence |
| SSP | System security plan recorded per control; Word export in NIST SP 800-171 format |
| Evidence | Tasks bound to AOs, direct upload, AI batch classification, agent-collected technical evidence |
| Self-assessment score (SPRS) | Per-AO compliant/non-compliant verdicts with automatic scoring |
| POA&M | Non-compliant items flow into the remediation plan with reminders; closing requires evidence |
| Year over year | Each cycle inherits the last; surveillance updates only what changed |
Workflow
- Inventory objectives
- Write the SSP
- Collect evidence
- Internal self-assessment
- Remediate
- C3PAO readiness
- Closing report
Frequently asked questions
If your customer sits in the US defense supply chain, the contract will require the matching level. Level 1 is self-assessed; most Level 2 needs a third-party assessment.
Related guides
Go to the compliance guides →