Start from compliance; see accountability and risk across the company
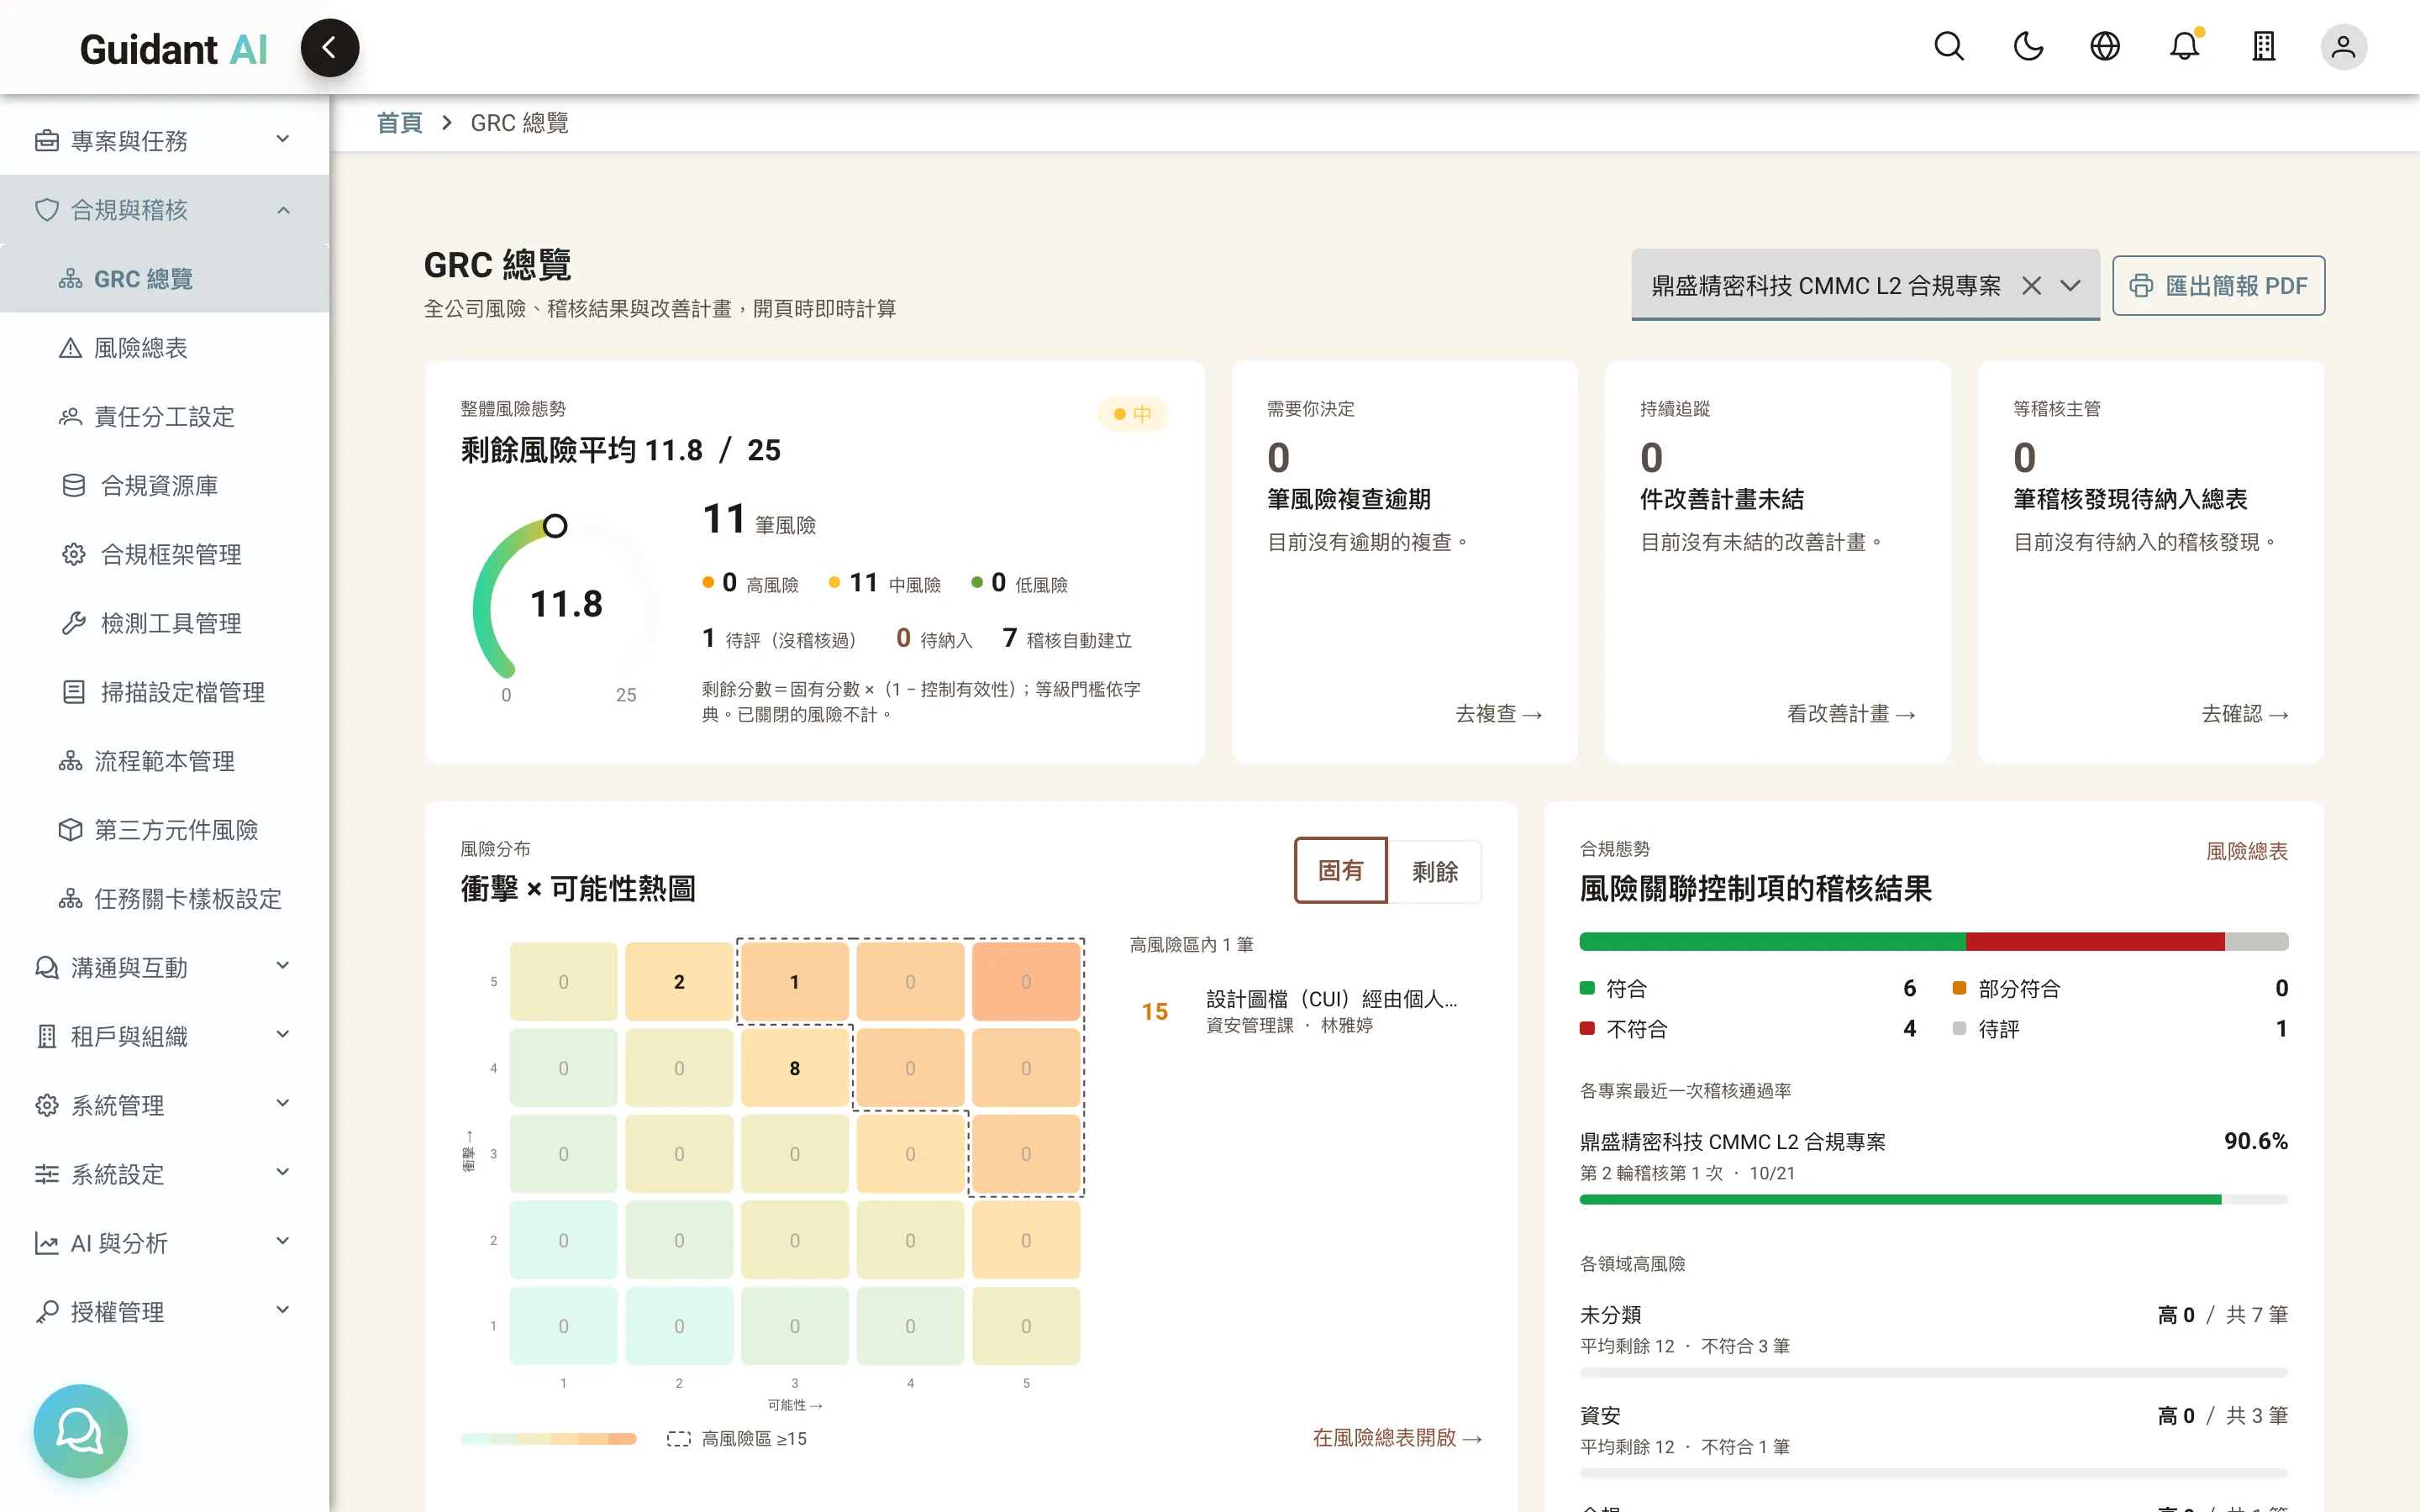
Departmental responsibility matrix, risk register with heat map, and a one-page executive overview. Get compliance right and governance and risk follow.
The problem
The compliance project is done and the CEO asks, "So where are our risks? Which department is weakest?" No answer — the data is scattered across projects. The GRC module rolls project results up to company level.
01
Responsibility matrix (RACI)
For every control: who's responsible, who approves, who's informed
Map the department tree to controls and set a RACI default; new projects apply it automatically. The accountability summary in the closing report comes straight from here.
02
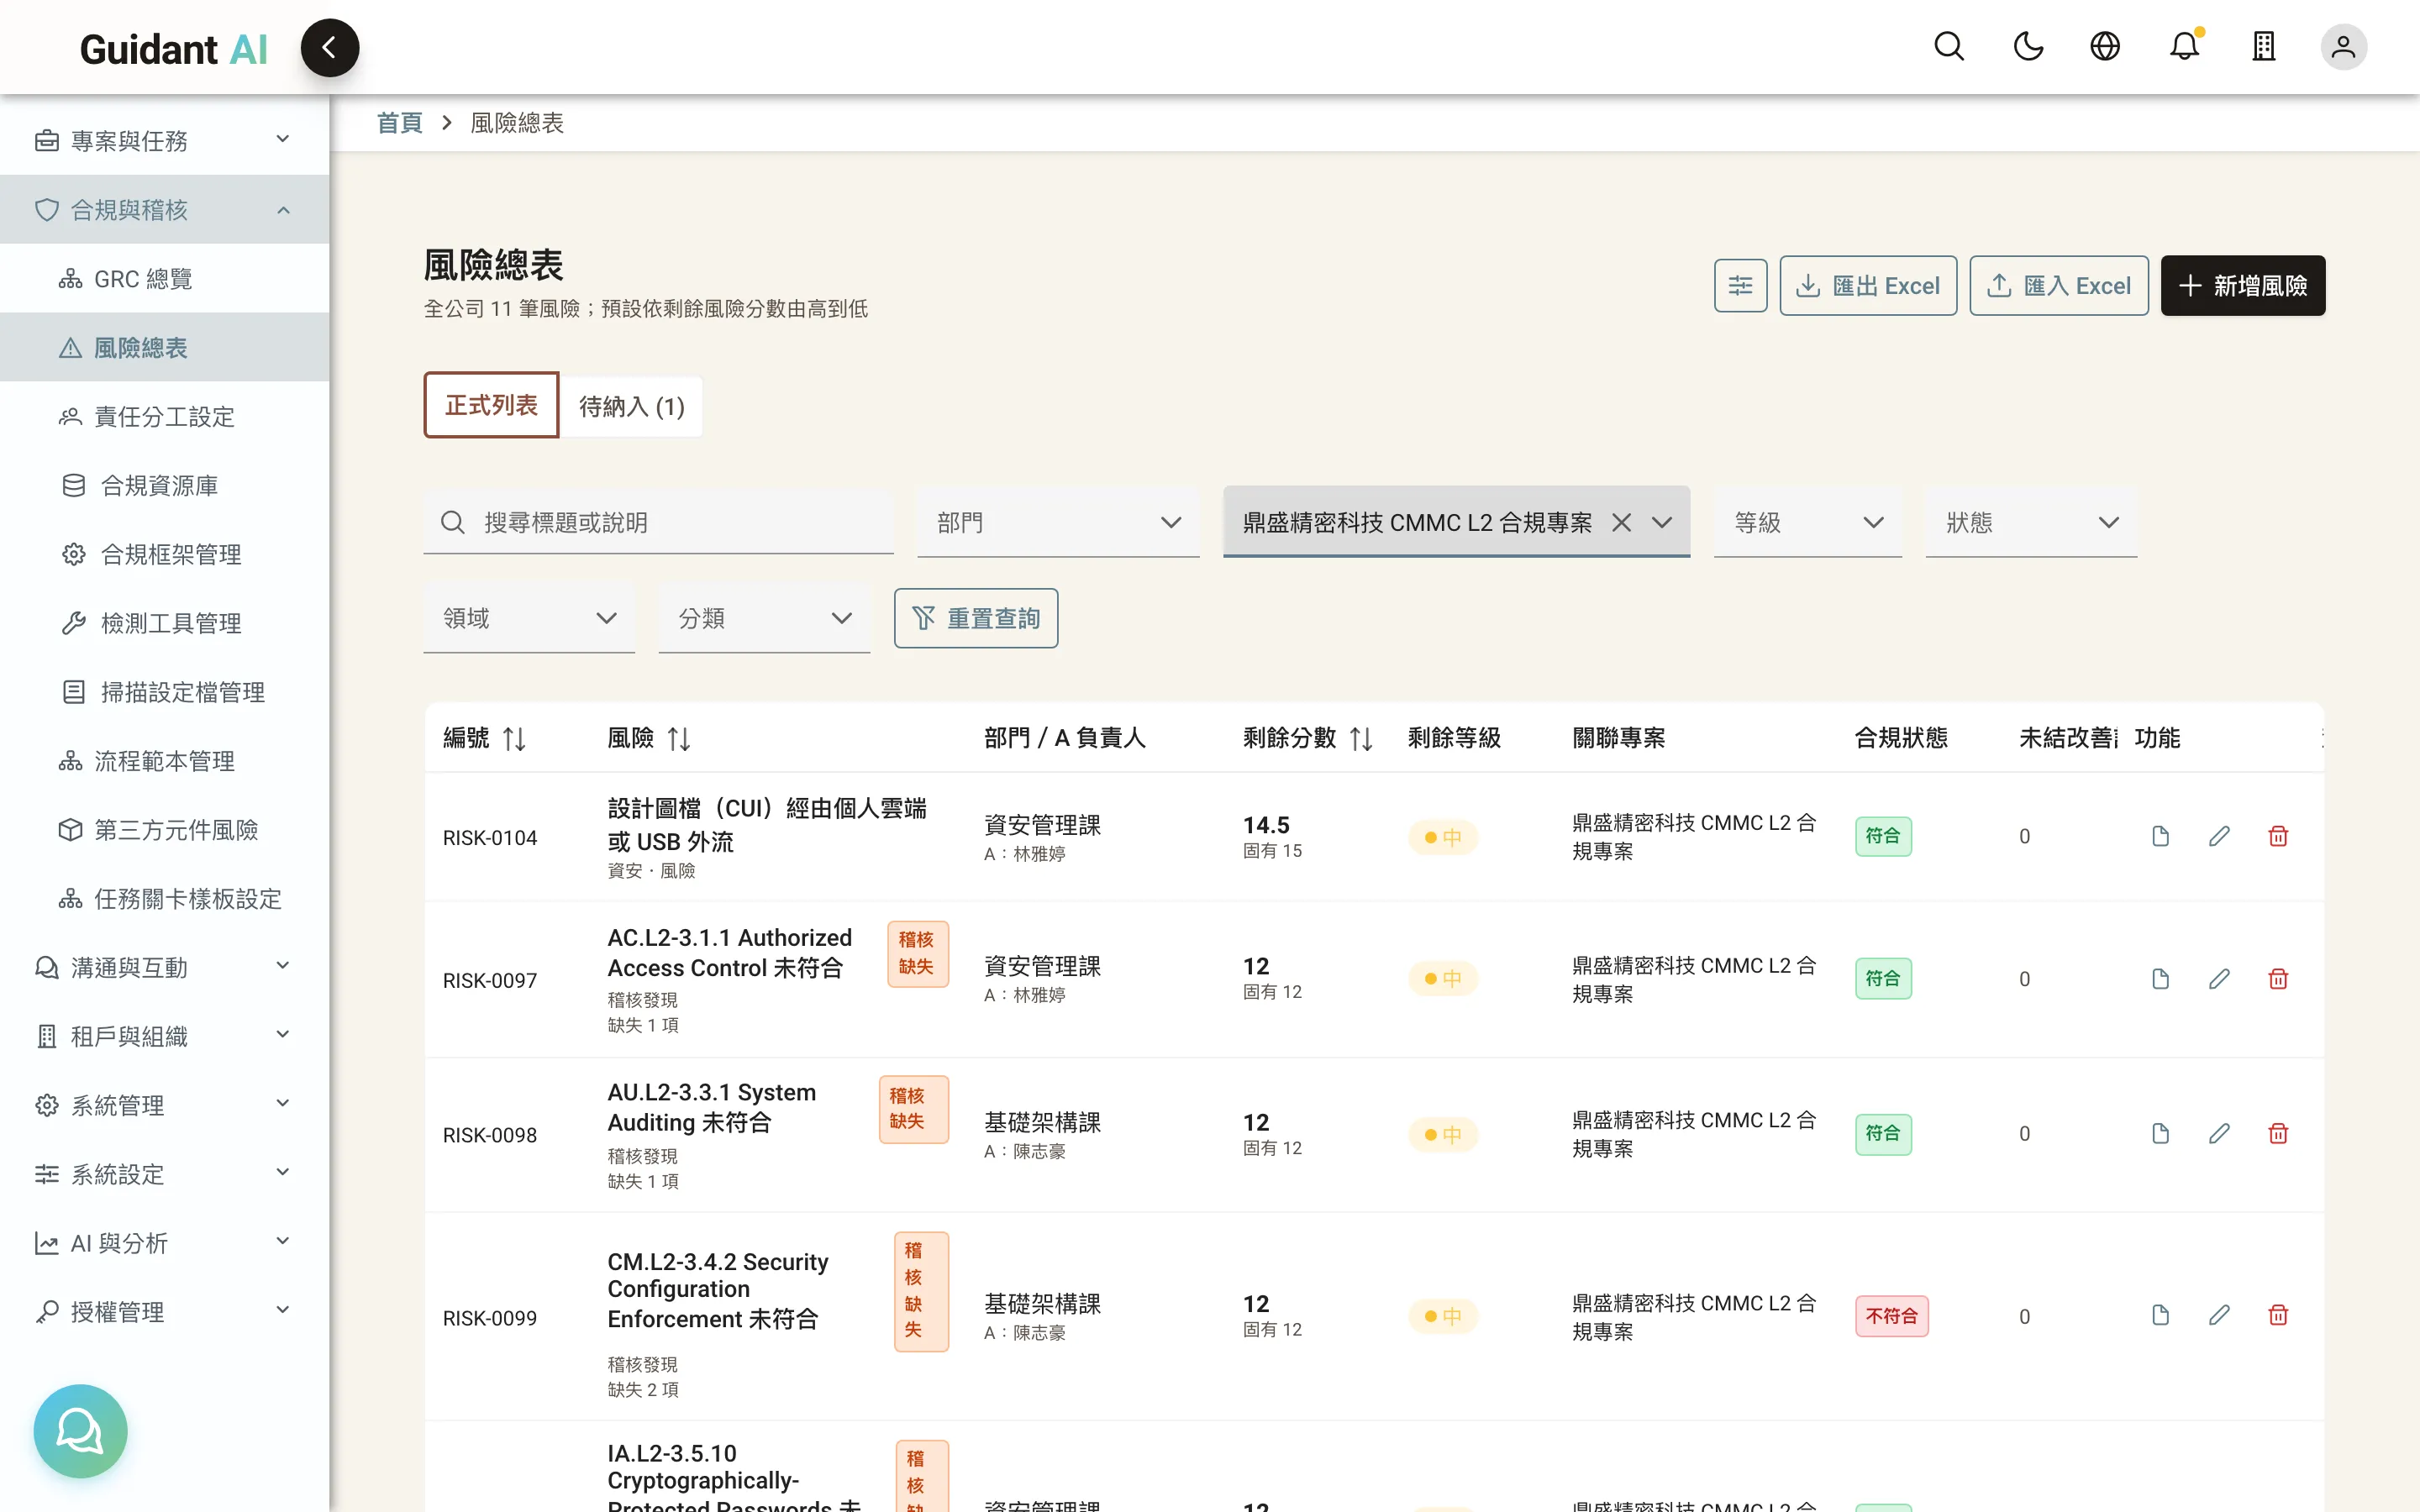
Risk register and heat map
What fails the audit becomes a risk automatically
Company-wide risks in one table: source, scope, likelihood, severity, treatment, acceptance sign-off. A 5×5 heat map shows where they cluster. A "non-compliant" verdict can be registered as a risk in one click.
03
GRC overview
The one page for executives
Department scorecards, completion by framework, open high risks, overdue remediation. Put this page on the screen and the meeting is covered.